Six national physician organizations warned that claims of AI superiority undermine patient trust, putting new attention on how practices set rules for AI use by clinicians and staff.
An artificial intelligence vendor contract may cap what the company owes the practice, but health care attorney Tatiana Melnik, J.D., says the people using the tools are the bigger risk.
Health care attorney Tatiana Melnik, J.D., gives practice administrators the same first assignment whether they are buying a new artificial intelligence (AI) tool or already running one: pull the
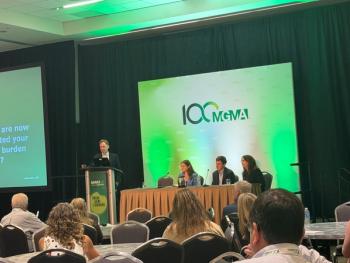
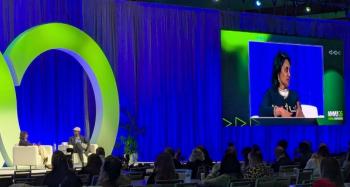
Melnik, of Melnik Legal PLLC in Tampa, Florida, represents physician practices. She presented "Privacy and Security Legal Issues in the Age of Artificial Intelligence" on Sept. 28 at the Medical Group Management Association (MGMA)
Allowing a vendor to de-identify patient data may have been a low-risk choice before AI. Today, Melnik said, a practice might decide it's high risk "because re-identification is so easy."
She advised administrators to look closely at how a contract defines "usage data," normally the clicks a vendor tracks to troubleshoot its product, and to ask whether AI prompts now fall under it. The same goes for "confidential information," any right to keep data after termination and the vendor's obligation, and ability, to delete it.
If a vendor can't delete the data, Melnik said, the next stop is the indemnity and damages cap language. Many contracts limit the vendor's liability to 12 months of fees paid before an incident. "Well, if the incident arises three years after the contract because you've allowed them to keep your data post termination, then the damages cap is zero," she said. That leaves the practice, as the HIPAA covered entity, holding the liability.
Asked for one step an administrator could take right away, Melnik said, "Train your team. Spend the money necessary to actually train your staff." She suggested weekly five-minute sessions on best practices, weekly reminders on existing policies and ongoing training beyond that.
"The biggest risk in a lot of these technologies is the people using them," she said. "It's uncomfortable. It takes time. No one wants to do it. People don't remember, and that's why you've got to do it anyway."
Patients in California have brought consumer class actions against practices and hospital systems over
Her advice is to get patients' affirmative consent and decide ahead of time what happens when a patient refuses. The practice can turn the tool off for that patient, or it can make the technology a condition of care, as some practices did with electronic records. Either way, she would put the AI disclosures in the existing notice of privacy practices, a document HIPAA already requires.
Physicians Practice was in San Antonio at the MGMA Annual Conference, Sept. 27-30, celebrating 100 years of MGMA, attending sessions and speaking with industry leaders. Follow our coverage on our