

It doesn't matter how small or big your practice is, you need to be prepared for ransomware attacks.

It doesn't matter how small or big your practice is, you need to be prepared for ransomware attacks.
In doing research for an upcoming conference, this doctor discovered three interesting trends on the use of social media by patients and providers alike.
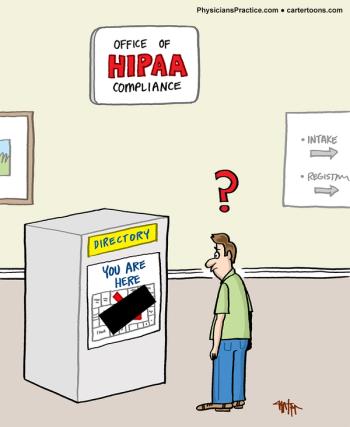
Can a practice be TOO committed to HIPAA? In this case of this organization, the answer to that question might be a somewhat confusing yes.
Recent ransomware attacks and the Phase II Office for Civil Rights Audits underscore the importance of adequate policies and procedures.
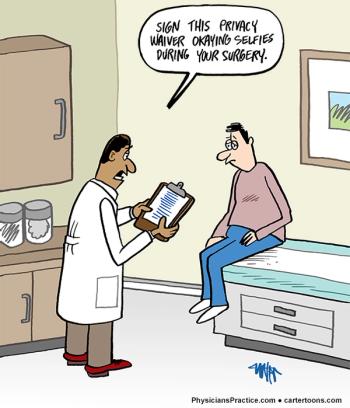
One doctor has found a clever way to bypass HIPAA and allow patients to take selfies during their surgery. What's his secret?
HIPAA can be a headache for patients, too. Here are some things you can do to calm the waters when patients object to HIPAA restrictions.
The ins and outs of when you can legally disclose patient information and when you can't aren't always obvious. Here's a little guidance.
Does your collections agency have the specialized knowledge needed to get the most ROI on your delinquent accounts? Here are the seven questions to ask. [Sponsored]
Asset protection shouldn't just be limited to malpractice. Here's why you need to looking beyond just that one area.
The top reasons healthcare data is breached are totally avoidable through low-hanging methods of security.
We often think of IT departments when we think of meeting HIPAA regulations, but the heart of compliance is in human resources.
Even if you're totally HIPAA compliant and know that your portal is secure, your patients may not be so sure.
A perfect storm of HIPAA audits and an increasing threat from hackers could spell disaster for your practice. Avoid this fate.
Despite HIPAA protections, young adults still on parents' health policies have little privacy. In some states, that is beginning to change.
Different types of data breaches at two hospitals in Michigan and New Mexico underscore HIPAA liability concerns.
Some HIPAA violations can be caught and fixed before the damage is done. Here are a few ways to do so.
Some HIPAA violations are obvious, but others can be less so and easy to miss. Here are four.
Password security isn't just for providers. Practices should make sure its patients are using tough passwords when using their patient portal.
It's important that physician practices stay compliant with HIPAA by executing business associate agreements with various vendor partners.
Choosing good passwords and protecting them is a small but key part of guarding your patients’ protected health information.
No practice is too small to not worry about a cyberattack. Here are four reasons you should be concerned that your EHR is at risk.
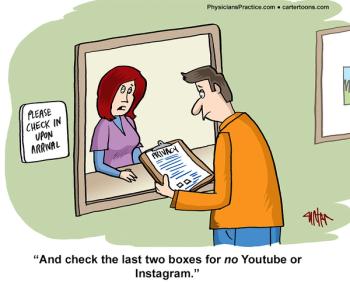
One practices has figured out a way to keep their patients from breaking HIPAA rules and using social media when they are in the exam room.
Before you decide to create your killer mobile health app, this lawyer advises you look at the FTC's guidance on developing one.
Here’s what you do when a HIPAA violation affects your patients, but is the fault of one of your business partners.
Lost laptops, tablets, and phones are among the most common ways patient privacy is breached. Here’s what to do if it happens to you.