
Many physicians feel that useless chart documentation has grown to consume most of the patient visit, leaving little time for patient care.
Many physicians feel that useless chart documentation has grown to consume most of the patient visit, leaving little time for patient care.
Practice owners should be leery of potential financial fraud, which seems to peak at the end of the year. Here are some things to look out for.
When it comes to HIPAA breaches, entity size does not matter. What matters is the Office for Civil Rights (OCR)’s oversight and compliance.
It’s important to not cut corners when assessing the cost of a new technology and forget about its potential security threats.
Two recent articles underscore the importance of cybersecurity across all facets of a physician’s practice and what questions should be asked.
Technology tools, like Apple’s ResearchKit, present exciting opportunities for healthcare, but they must be regulated to protect personal health data.
Physicians want access to patient data on the go, but practices need to have a secure BYOD policy. Here are a few steps to protect data within the EHR.
Practices are more at risk for breaches than ever before. Here are a few steps to protect data in the EHR and elsewhere.
Having a data breach response plan on paper isn't enough. Practice staff expected to implement it must understand and be equipped to execute their tasks.
Our 2015 Technology Survey Sponsored by Kareo reveals common challenges practices face after technology implementations. Here's what they are, and how to address them.
For PHOs and super groups, one practice's misstep to put everyone at risk. Here are six potential threats to avoid and the best way to stay safe.
A couple of words can mean the difference between being covered for a certain event and not being covered.
HIPAA may actually be harmful as it distracts attention and diverts resources away from those actions that might actually improve privacy and security.
The OIG fraud alert warns physicians to be wary of compensation arrangements that could violate the Anti-Kickback Statute.
Doctors have a lot of valuable personal and professional data on their laptops and other devices. Here are five simple ways to keep that data secure.
Physicians should be aware that Phase II of OCR's HIPAA Audits have commenced. Here is a short check-list to prepare your practice.
Experts say there are common compliance misconceptions that are costing practices unnecessary time and resources.
Under the HIPAA Omnibus Rule, patients can request a restriction on disclosure of PHI to a payer if they pay out of pocket, in full for a service.
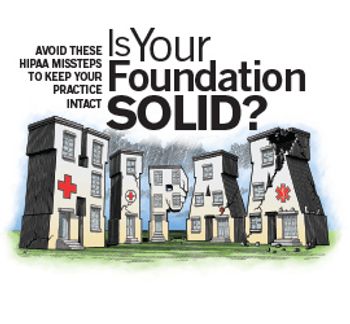
Nine HIPAA missteps that experts say medical practices make every day.
Cyber risk isn't just a technology issue. It affects your entire business, so have a plan in place and mitigated through education and risk management.
Recent court rulings underscore the importance of maintaining compliance with Medicare billing.
When physicians and other entities resist complying with HIPAA requirements, it can lead to an increase in practice liability.
Before you fire off a response to a negative patient review, here are seven things to consider. You don’t want to post something potentially worse online.
TAP - technical, administrative, and physical controls should form the foundation of HIPAA compliance.

Step up HIPAA compliance by identifying what's getting other practices into trouble, and taking steps to avoid making the same mistakes.